You're shipping faster than ever. So are the attackers.
A few years ago, building an app meant weeks of work. Today you hand a coding agent a prompt, a spec, or a loop, it burns some tokens, and out comes a working app. Agentic engineering and vibe coding have made everyone a developer.
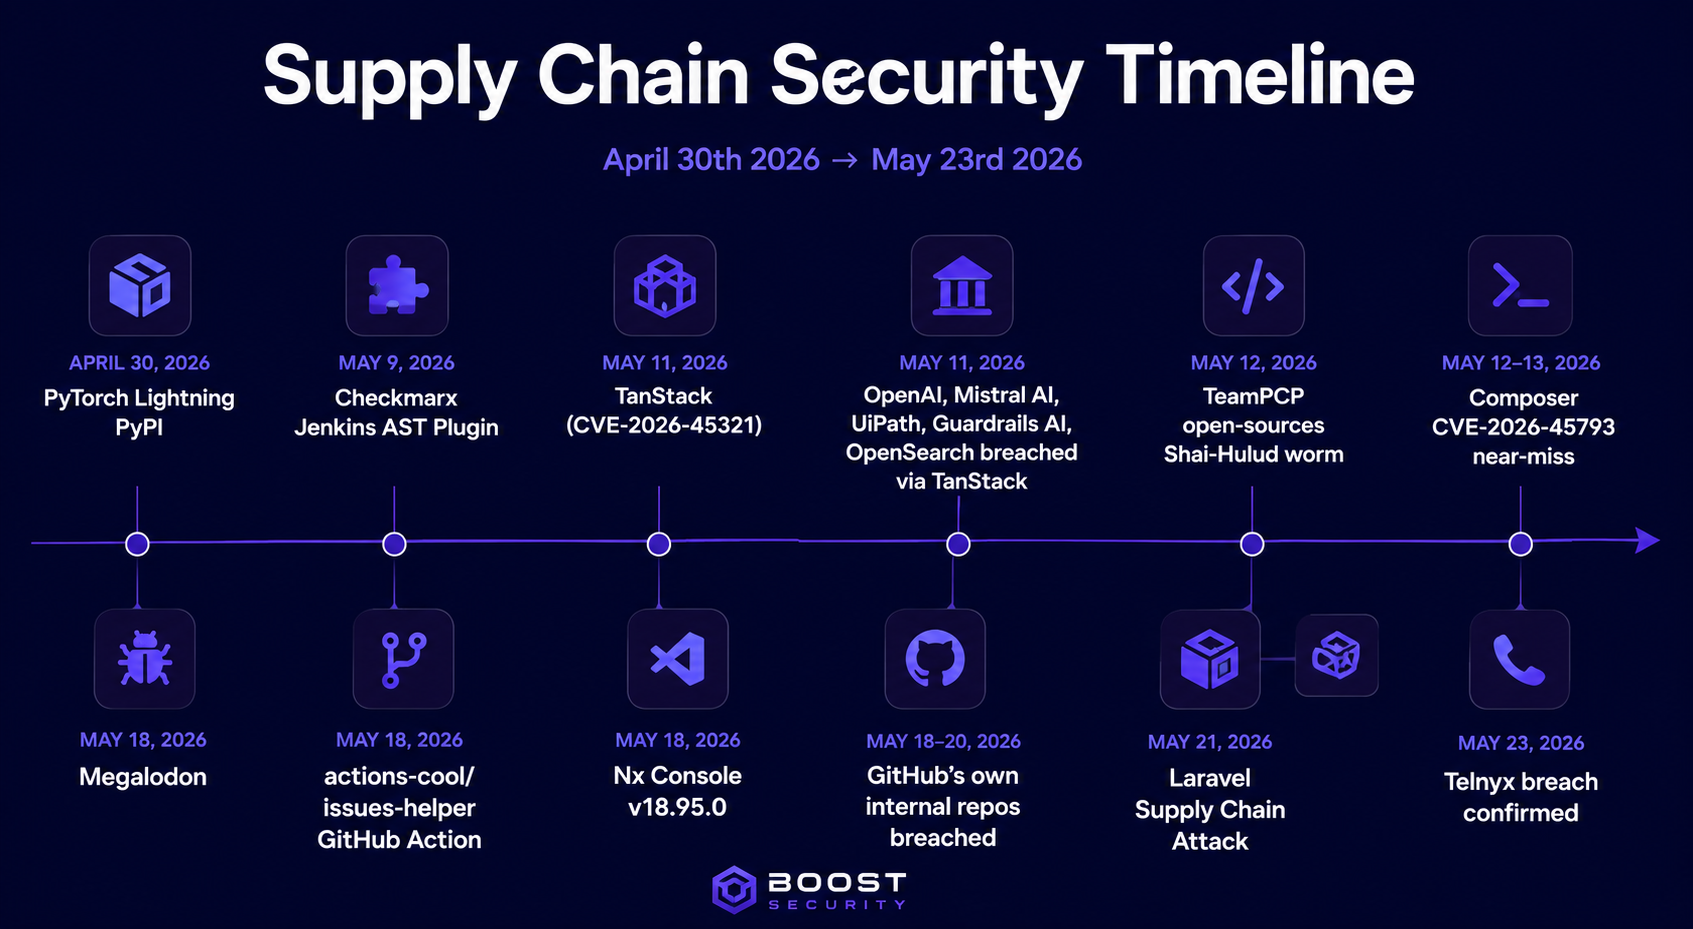
The catch: every one of those steps pulls in dependencies, and some of them are malicious. Hundreds of malicious packages land on public registries every month, and the people planting them are getting craftier about how they slip in. Your agent will not notice. Neither will you, until it is too late.
It only takes one bad dependency. Once it runs, you, your machine, and everyone who collaborates on your projects are exposed to a software supply chain attack.
Meet Dazio
Dazio is a free tool from BoostSecurity that protects developers and their coding agents against software supply chain attacks. It blocks malicious packages before they install, finds the ones already on your machine, cleans up the secrets attackers are after, and hardens the tools you and your agents build with.
We built it because we think the world needs one. Software development got dramatically faster; the safety net did not keep up.
What Dazio does
Three things, in order of how much they matter when an attack is underway.
1. Detects and stops malware. Dazio blocks malicious dependencies at install time, before they ever run. It also scans the projects already on your machine and flags any that reference known-malicious packages.
2. Cleans up your secrets. Secrets are what supply chain malware is really after: your LLM API keys, your GitHub tokens, your cloud credentials. They end up in places you forgot about: a .env left in a project, a markdown file an agent wrote, your shell history. Dazio finds them so you can move them into a password manager or secrets vault, or follow industry best practice to use ephemeral tokens linked to machine identity instead or PassKey reprompt.
3. Hardens your dev toolchain. The tools you and your coding agents use every day ship with settings that can make them considerably safer. Dazio surfaces those hardening opportunities so you can turn them on in minutes instead of discovering them after an incident.
How it works
You can use Dazio two ways.
Run a one-time scan. Dazio walks your home folder for development projects and reports three things: secrets sitting in the open that belong in a password manager, references to malicious dependencies, and ways to tighten your development environment. It is a good way to see where you stand today.
Install the daemon. For real protection, run Dazio as a background daemon. It checks every package across every install, regardless of which package manager or project pulled it, and blocks malware before it lands.
If you change your mind, uninstalling takes one command.
Aren't there other free package firewalls?
There are. We tried them, and they fall short in three ways.
Coverage. Most free firewalls only watch Python and JavaScript. Dazio also covers Ruby, Rust, and Go today, with .NET (NuGet) and Java (Maven) on the way.
Depth. Supporting an ecosystem on paper is not the same as supporting how people actually use it. Some tools handle pip but miss installs inside a virtualenv. Others have never heard of uv or uvx. Dazio follows the package wherever it is installed from.
Threat intelligence. Several free tools expect you to bring your own feed or rely on an open-source one, and those feeds can run a day or two behind or miss things entirely. Dazio ships with the same enterprise-grade feed we use with our customers, updated hourly. A day is a long time when a malicious package is live on a registry.
Why give it away?
Because the people who need it most are not going to buy a security product. We have friends and family building new and amazing apps with AI, and most of them have never heard the phrase "supply chain attack." We would like them to keep building, and to face fewer and smaller incidents while they do.
We also have a long history of releasing free tools, some of them open source. Dazio is free to use; it is not open source.
If you are an enterprise and need governance, advanced reporting, enterprise support and more on top of this, that is our Developer Endpoint Security product. Talk to us to learn more.
Get started
Head over to boostsecurity.io/dazio, follow the easy setup instructions, and run your first scan to see where you stand.