
Lock Down the Agentic Workspace.
Attackers moved upstream to the laptop. Lock down the workstation, govern the AI coding tools on it, and strip secrets from your developers' prompts before anyone commits code.
Discover Your AI Attack Surface →


You Can't Protect the Software Factory If You Can't See the Machines.
AppSec teams who can only see the CI/CD pipeline catch attacks too late. Attackers now hit the machine first, and can go undetected by your stack.
Developers Install Coding Tools.
AI Assistants Leak Your Keys.
Malware Runs Before Code Is Reviewed.
Govern Every Device Writing Your Code.
Boost secures your developer machines, governs the AI tools on them, and enforces your policies in devs' workflows at the moment code is written (by your devs or their coding agents).


Key Capabilities
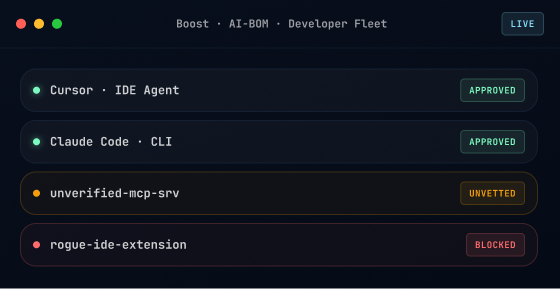
Map the AI-BOM. Control the Toolchain.
Stop flying blind. Boost continuously maps the "AI-BOM" of your developer fleet. We detect active coding agents (Cursor, Windsurf), MCP servers, local models, and IDE extensions. We validate connections and block unvetted tools to prevent silent drift from your security baseline.
Kill the Blast Radius. Protect the Prompt.
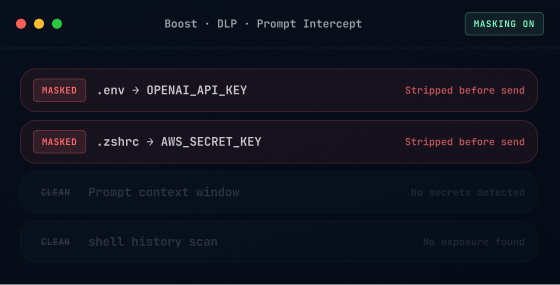
Your API keys do not belong in a model's training data. Boost intercepts outbound prompts mid-flight, masking credentials and sensitive data. We also scan the local environment for exposed secrets in config files and shell history, locking down the machine before an attacker can pivot.
Inject Security at the Point of Generation.
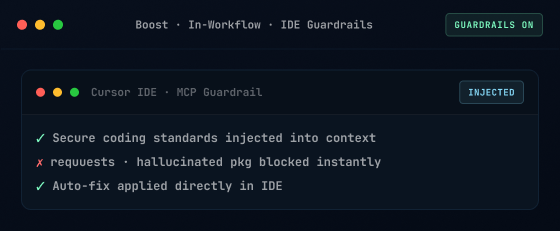
Prevention beats remediation. Boost injects your secure coding standards directly into the agent's context window. The AI knows what is allowed before it starts typing. We block hallucinated packages the millisecond a download is attempted and auto-fix vulnerabilities directly in the IDE.
One Platform
Covers Laptop, Repo And Pipeline.
Boost links the machine, the code, and the production environment.
AppSec + Endpoint + Supply Chain
Distributed Policy Enforcement
Cover What EDR Doesn't See
We Cover the Tools Devs Already Use.
- Full Model Context Protocol (MCP) server monitoring and governance
- Exposed secrets, dotfiles, environment variables
- Homebrew packages
- Malicious IDE and browser extensions
Stop Guessing What's Running on the Endpoint.
Deploy Boost to map your AI-BOM and instantly discover the unmanaged agents, rogue MCP servers, and exposed secrets sitting on your developer laptops right now.